
TL;DR

Get privacy and security gear delivered free — and shop member deals
- Fast, free delivery on millions of items
- Access to Prime Big Deal Days deals on October 6–7
- Prime Video, Amazon Music and more included
Yarbo has committed to removing its default remote backdoor in its robot lawn mowers, making it an opt-in feature for users. This change follows security concerns and promises greater user control over device access.
Yarbo has announced it will remove the default remote backdoor from its robot lawn mower, making remote access an opt-in feature for users. This move aims to address security concerns raised by researchers and improve user control over device access.
Initially, Yarbo’s company representatives indicated that the remote backdoor, which could be exploited by malicious actors, would remain in the devices to assist with troubleshooting, but with additional protections. However, following scrutiny and security research, Yarbo’s co-founder Kenneth Kohlmann confirmed that the company will now implement a system where users can opt in to enable remote access.
The company plans to make the backdoor an optional feature that users can activate if needed, rather than a default setting. This involves a setup script that remains inactive until triggered by the user, who can then decide whether to enable remote troubleshooting capabilities. The change is part of Yarbo’s broader effort to improve security, including issuing firmware updates to the first batch of 1,000 devices, each with a unique root password.
Why It Matters
This development matters because the previous default remote backdoor posed security risks, including potential hijacking and data exposure, which could compromise user privacy and safety. By making remote access opt-in, Yarbo enhances user control and reduces the attack surface, aligning with best practices for connected device security. The move also signals a shift towards greater transparency and responsiveness to security concerns in the IoT space.
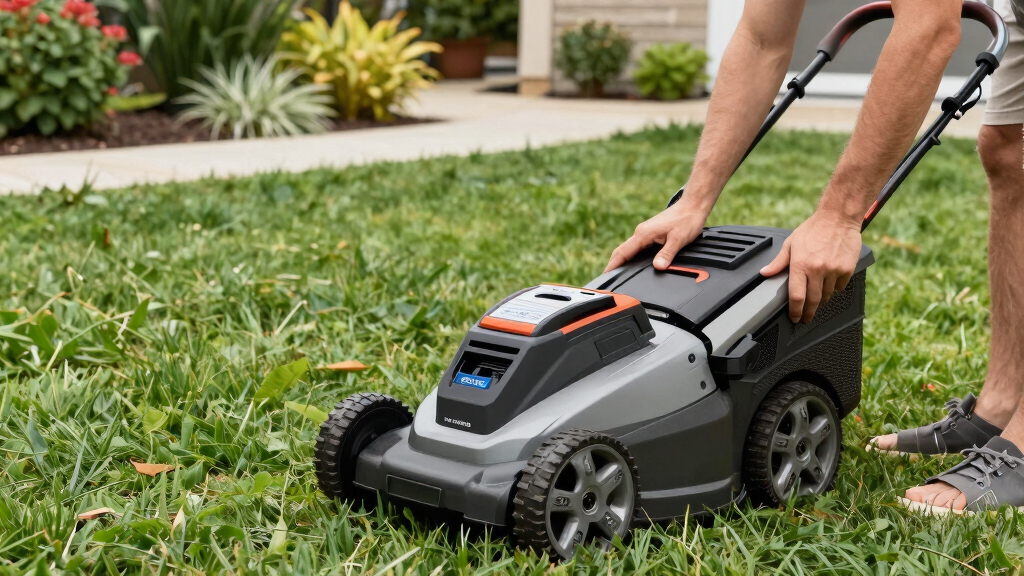
robot lawn mower with remote access
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Background
Yarbo’s robot lawn mower had previously been criticized after security researcher Andreas Makris demonstrated how it could be hijacked remotely, exposing email addresses and GPS locations. The company initially committed to fixing security flaws but maintained the remote backdoor for troubleshooting purposes. Following public scrutiny, Yarbo promised to close security gaps, and now, with this latest change, it is moving towards giving users more control over remote access features.
“In the future there should be no remote backdoor unless the user decides to opt-in.”
— Kenneth Kohlmann, Yarbo co-founder
“Completely removing remote diagnostic capability would reduce our ability to help customers resolve safety, connectivity, and service issues quickly.”
— Showan Hou and Maggie Zhou, Yarbo spokespeople
security features for robot lawn mowers
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
What Remains Unclear
It is not yet confirmed how quickly Yarbo will fully implement the opt-in system across all devices, or whether users will have the ability to disable the backdoor permanently after enabling it. The effectiveness of the upcoming security measures and whether they will satisfy all security concerns remain to be seen.
Yarbo robot lawn mower firmware update
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
What’s Next
Yarbo plans to roll out firmware updates that implement the opt-in remote access feature across current and future devices. The company is also in contact with security researcher Andreas Makris, who may validate the security improvements. Further updates will clarify the timeline and user options for remote access control.
As an affiliate, we earn on qualifying purchases.
Key Questions
Will the remote backdoor be completely removed from all Yarbo robots?
Yarbo has announced it will make remote access an opt-in feature, effectively removing the backdoor by default. The process involves a setup script that remains inactive unless triggered by the user.
Can I still get remote support if I choose to disable the backdoor?
Yes, Yarbo states that users can opt in to enable remote troubleshooting when needed, but the backdoor will not be active by default.
When will the firmware updates be available?
The company has already begun rolling out firmware updates to the first batch of 1,000 devices, with plans for additional waves. Exact timelines for all devices are still being finalized.
Does this change affect the security of my device?
Making remote access optional and implementing unique root passwords are intended to enhance security and reduce vulnerabilities. However, the full impact will depend on the implementation and user choices.
Fall Picks
fall essentials
As an affiliate, we earn on qualifying purchases.