TL;DR
Security experts have confirmed that attackers are actively exploiting CVE-2026-8037, a command injection vulnerability in Progress LoadMaster. The flaw allows unauthenticated attackers to execute arbitrary commands on affected appliances, raising urgent security concerns.
Security researchers have confirmed that CVE-2026-8037, a command injection vulnerability in Progress LoadMaster, is being actively exploited by attackers. This flaw allows unauthenticated attackers to execute arbitrary commands on affected appliances, posing a significant security risk. The confirmation of active exploitation underscores the urgency for affected organizations to assess and mitigate their exposure.
Progress LoadMaster, a widely used application delivery controller, contains a command injection vulnerability that can be exploited without authentication, according to a CISA alert. The flaw resides in the handling of unsanitized input in the load balancer’s management interface, enabling attackers to run arbitrary system commands remotely.
Cybersecurity firms and government agencies have reported that malicious actors are actively exploiting this vulnerability in the wild, targeting organizations with vulnerable LoadMaster appliances. The attacks could lead to full system compromise, data theft, or disruption of services. The vulnerability is tracked as CVE-2026-8037.
Implications of Active Exploitation on LoadMaster Security
The active exploitation of CVE-2026-8037 significantly increases the risk for organizations using Progress LoadMaster. Because the flaw allows unauthenticated command execution, attackers can potentially gain persistent access, escalate privileges, and compromise entire networks. This vulnerability highlights the importance of timely patching and robust security measures for critical infrastructure components.

The Practice of Network Security Monitoring: Understanding Incident Detection and Response
- Condition: Used Book in Good Condition
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Background and Discovery of CVE-2026-8037
The vulnerability was identified by security researchers during routine assessments of LoadMaster appliances. Progress Software issued a security advisory in recent days, confirming the flaw and urging users to apply updates. The flaw stems from improper input validation in the management interface, which attackers can exploit remotely.
Prior to this, LoadMaster had a history of security issues, but CVE-2026-8037’s active exploitation marks a new and urgent threat. The vulnerability is listed under CVE-2026-8037 and has received a high severity rating from security agencies.
“The exploitation of CVE-2026-8037 poses a significant risk to organizations using Progress LoadMaster. Immediate action is recommended.”
— CISA
AI-POWERED CYBERSECURITY OPERATIONS: Threat intelligence anomaly detection and automated incident response systems
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Unresolved Aspects of the Ongoing Exploits
Details about the full scope of the active attacks, including the number of affected organizations and specific methods used by attackers, remain unclear. It is also not confirmed how widespread the exploitation currently is or whether additional vulnerabilities are being leveraged in conjunction.
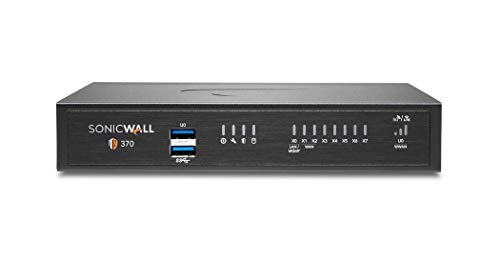
SonicWall TZ370 Gen7 Firewall | Advanced SMB Security Appliance with Multi-Gigabit (2.5/5 G) Interfaces, SD-WAN, and Real-Time Threat Defense (02-SSC-2825)
- Product Type: SonicWall TZ370 Firewall Appliance
- Subscription: No Service Subscription Included
- Target Audience: Designed for Growing SMBs
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Next Steps for Mitigation and Monitoring
Organizations using LoadMaster should prioritize applying the latest security updates provided by Progress Software. Security teams are advised to monitor network traffic for signs of exploitation and to implement additional security controls. Further details about the scope of the attacks and mitigation strategies are expected from vendors and cybersecurity authorities in the coming days.

Network Vulnerability Assessment: Identify security loopholes in your network's infrastructure
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Key Questions
What is CVE-2026-8037?
CVE-2026-8037 is a command injection vulnerability in Progress LoadMaster that allows attackers to execute arbitrary commands without authentication.
How are attackers exploiting this vulnerability?
Attackers are exploiting the flaw by sending specially crafted requests to the LoadMaster management interface, which does not properly sanitize input, enabling remote command execution.
What should affected organizations do now?
Organizations should immediately update their LoadMaster appliances with the latest patches from Progress Software and monitor their systems for signs of compromise.
Is there a fix available yet?
Progress Software has issued security advisories and is working on providing patches. Affected users should check for updates and apply them as soon as they are released.
How widespread is this issue?
The full extent of the exploitation is still being assessed, but active attacks have been confirmed, emphasizing the need for urgent mitigation.
Source: kev