
TL;DR

Get privacy and security gear delivered free — and shop member deals
- Fast, free delivery on millions of items
- Access to Prime Big Deal Days deals on October 6–7
- Prime Video, Amazon Music and more included
A hotel check-in system called Tabiq, operated by Reqrea in Japan, left over one million customer documents accessible online due to a misconfigured cloud storage bucket. The data is now secured after TechCrunch alerted the company. The incident highlights ongoing cybersecurity risks from human error and misconfigurations.
A hotel check-in system operated by the Japan-based startup Reqrea exposed over one million passports, driver’s licenses, and selfie verification photos due to a misconfigured cloud storage bucket, which has now been secured. The incident was revealed after security researcher Anurag Sen alerted TechCrunch, prompting the company to take action. The exposure underscores ongoing cybersecurity vulnerabilities stemming from human error.
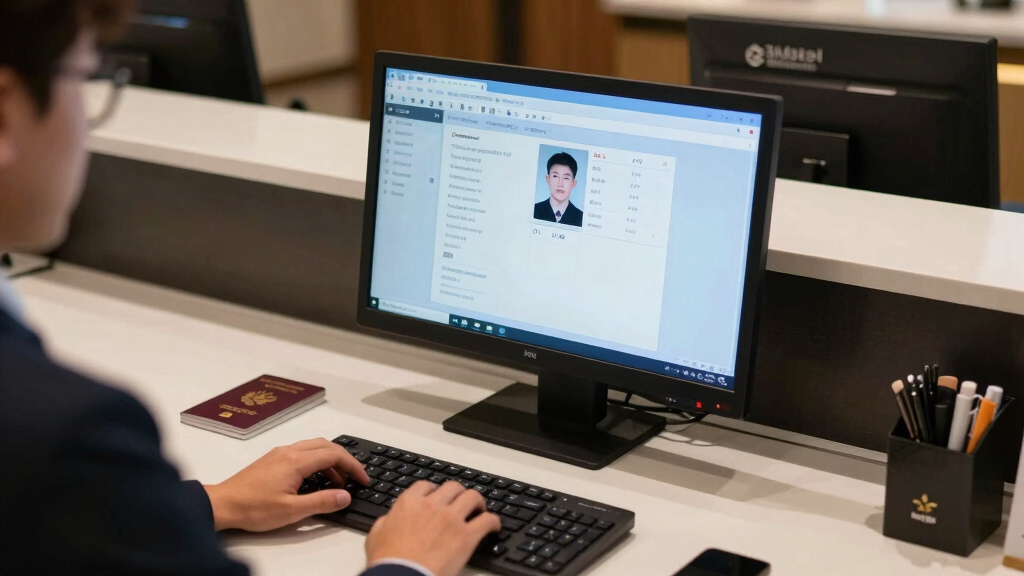
The hotel check-in platform, called Tabiq, relies on facial recognition and document scanning to verify guests. According to Sen, the company set its Amazon cloud storage bucket, used to store customer data, to be publicly accessible, allowing anyone with knowledge of the bucket name, ‘tabiq,’ to view the files without authentication. The data inside includes passports, driver’s licenses, and selfie verification images from guests worldwide, dating back to early 2020.
After being alerted by TechCrunch, Reqrea locked down the storage bucket. The company confirmed it is conducting a full review with external legal counsel to determine the full scope of the exposure and plans to notify affected individuals once the investigation concludes. It remains unclear whether anyone accessed the data before it was secured, although logs are being reviewed. The incident was also documented by GrayHatWarfare, a database that indexes publicly visible cloud storage, revealing the extent of the data leak.
Why It Matters
This incident highlights the persistent risks of data exposure caused by misconfigurations rather than sophisticated cyberattacks. The breach exposes sensitive personal information, increasing the risk of identity theft and fraud. It also emphasizes the importance of cybersecurity best practices, especially as businesses and governments rely more on digital identity verification methods, often involving sensitive documents.
As an affiliate, we earn on qualifying purchases.
Background
Previous incidents include breaches at services like Duc App and Hertz, where driver’s licenses and passports were also exposed. These lapses occur amid increasing use of identity documents for age verification and KYC processes, making data security critical. Amazon’s cloud platform has introduced safeguards to prevent such leaks, but human error remains a common cause of exposure.
“We are conducting a thorough review with the support of external legal counsel and other advisors to determine the full scope of exposure.”
— Masataka Hashimoto, Reqrea director
“The data was accessible to anyone with the bucket name, without any password or authentication.”
— Anurag Sen, security researcher
identity theft protection wallet
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
What Remains Unclear
It is not yet clear how many individuals may have accessed or downloaded the exposed data before the bucket was secured. The company is still reviewing logs to determine if there was any unauthorized access prior to the lockdown. The full extent of the data’s exposure remains unknown.
As an affiliate, we earn on qualifying purchases.
What’s Next
Reqrea will complete its investigation and notify affected individuals. The company is also expected to implement additional security measures to prevent future misconfigurations. Monitoring for any misuse of the exposed data will continue, and further updates are anticipated once the investigation concludes.
digital identity verification device
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Key Questions
How did the data become exposed?
The data was stored in an Amazon cloud storage bucket that was mistakenly set to be publicly accessible, allowing anyone with the bucket name to view the files.
What types of documents were exposed?
Over one million passports, driver’s licenses, and selfie verification photos of hotel guests from around the world.
Has the data been secured?
Yes, after TechCrunch’s alert, Reqrea locked down the storage bucket. The company is now investigating the full scope of the breach.
Could the data have been accessed by malicious actors?
It is possible, but it is not confirmed whether anyone accessed or downloaded the data before it was secured. Logs are being reviewed to determine this.
Fall Picks
fall essentials
As an affiliate, we earn on qualifying purchases.